 ER
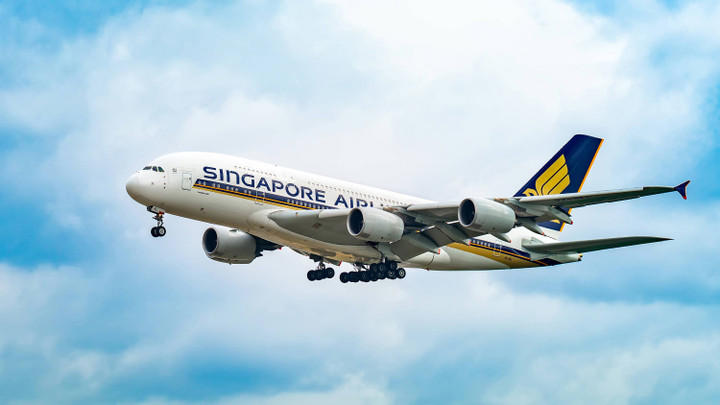
SINGAPORE Airlines (SIA) has experienced a cybersecurity incident that has drawn significant public attention. On Tuesday (11/03), 2026, approximately 46,000 flight booking records were accessed without authorization. The breach did not target SIA’s own IT systems, but rather the platform operated by Amadeus, the airline’s reservation technology provider.
According to The Economic Times, the airline stated that the accessed data primarily included customer names, booking reference numbers, travel itineraries, and booking classes. The incident has raised serious concerns, as it involves the personal data of a large number of passengers.
1. Details on the accessed customer data
CNA reported that, among the tens of thousands of affected records, approximately 620 entries may have included more detailed contact information. The sensitive data exposed in these instances includes email addresses, phone numbers, travel document details, and KrisFlyer membership numbers.
This additional level of access has heightened concerns regarding the potential misuse of the affected passengers’ personal information. Nevertheless, an initial assessment was promptly conducted to mitigate the risks involved.
2. Response from Amadeus and SIA
In response to the incident, Amadeus confirmed that no bank account or credit card information was compromised, and no bookings were altered. The company identified a vulnerability within its travel booking display environment, which has since been addressed, alongside strengthened monitoring and detection measures.
Meanwhile, SIA stated that it is contacting affected customers with upcoming travel plans to update their booking reference numbers as a precautionary measure. The airline has also notified the relevant authorities and reaffirmed its commitment to data security.
“The protection of our customers’ personal data is of the utmost importance to SIA,” the airline stated, as quoted by VnExpress.
3. Other airlines and authorities also affected
The impact of this data leak has extended to other airlines, involving data processed between August 2023 and September 2026. Affected carriers include Malaysia Airlines, Cathay Pacific Airways, Japan Airlines (JAL), Korean Air, and Asiana Airlines.
Cathay Pacific reported that approximately 53,000 bookings were impacted through the use of login credentials for the Amadeus system. Meanwhile, JAL reported that around 92,000 of its customers were affected, including those of its subsidiary, Japan Transocean Air.
In response to this incident, local authorities have begun taking official action. As reported by The Straits Times, the Personal Data Protection Commission (PDPC) has acknowledged the incident and is currently conducting an investigation. [IDNtimes/photo special]